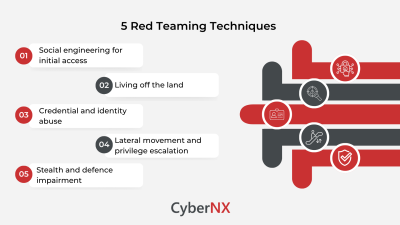
Red teams use adversary-focused techniques to replicate realistic attack paths and evaluate an organization's defenses. Common approaches include social engineering, living off the land, credential abuse, lateral movement, privilege escalation, and defense impairment. The findings can help organizations strengthen detection, response, and security controls.